
The Custom Web Application Development Process
A delivery process with clear decisions at discovery, prototype, implementation, acceptance, release and handover.
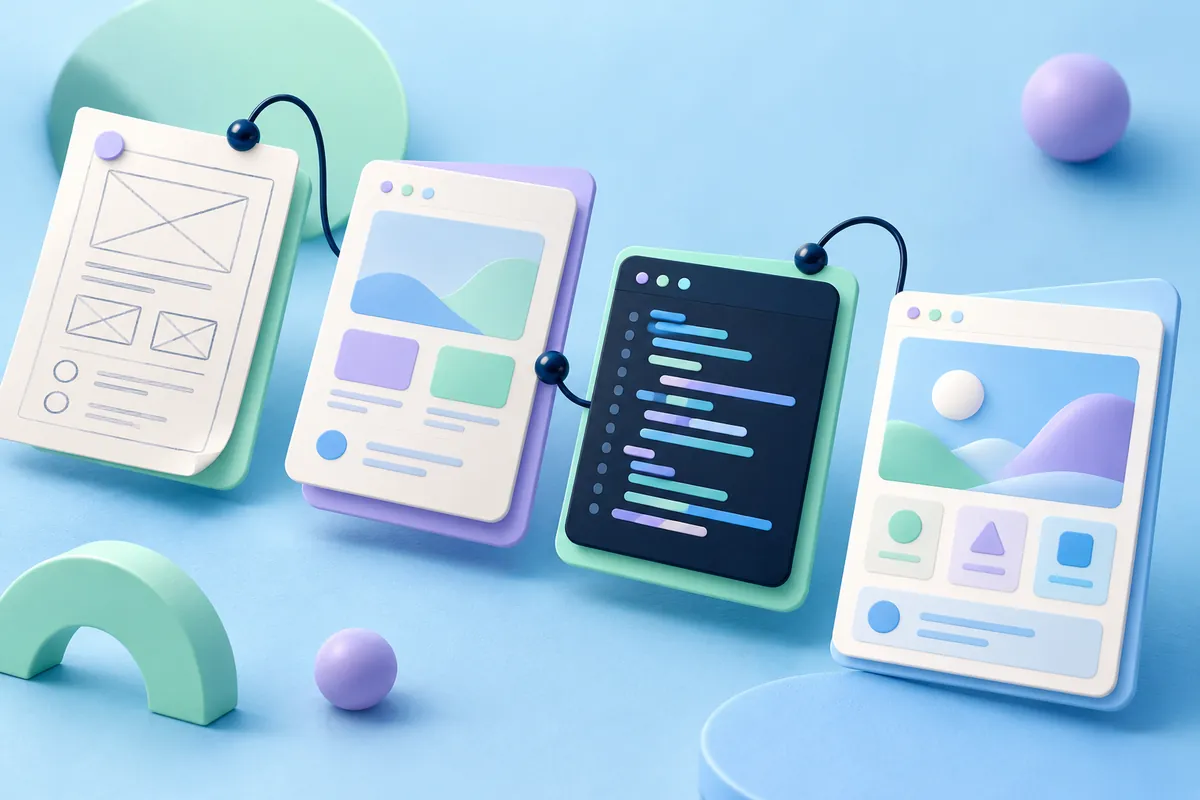
A useful development process makes uncertainty visible early and ties progress to working outcomes. The goal is not to produce documents for every activity, but to ensure the right people agree on what is being built and how it will be operated.
Discovery: define the problem and boundaries
Interview the people doing the work. Map the current process, systems, data and exceptions. Identify the business owner and the users who can approve a change. Write a bounded first-release scope and explicit non-goals. If an integration is uncertain, test it before promising a fixed delivery plan.
Prototype: test the difficult tasks
Use representative tasks and realistic sample data. Test error messages, long names, Thai text and mobile interaction as well as the ideal path. A prototype is for testing understanding and usability; it is not evidence that security or data persistence has been implemented.
Build: deliver complete slices
A slice should complete a useful journey, such as creating and assigning an enquiry with permission checks. Include validation, audit needs and failure handling in that slice. Show working increments to the business owner and keep scope changes explicit.
Acceptance: verify agreed outcomes
Turn the brief into test scenarios. Check access restrictions, duplicate submissions, failed integrations, exports and recovery. Use separate test data and production credentials. Automated checks are valuable, but a business user should also complete the workflows they will operate.
Release: prepare for an ordinary bad day
Document deployment, configuration, backups and rollback. Confirm who receives incident reports and who can access service accounts. Verify production SEO settings for public pages and noindex settings for previews. A successful build does not prove the correct build is serving the domain.
Handover: transfer operational capability
Provide code and data access as agreed, editor or operator training and a maintenance plan. Record known limitations and how future changes are requested. Hidden software costs explains why these responsibilities belong in the original plan rather than appearing as surprises after launch.
Sources & further reading
- Application Security Verification Standard — OWASP
- Backup and recovery — PostgreSQL
- SEO Starter Guide — Google Search Central
Examples and decision frameworks are planning guidance, not guaranteed outcomes. Check current provider requirements before implementation.
Related articles
View all →
Custom Software
What Is Custom Software Development?
Understand when tailored software is justified and what discovery, delivery, ownership and maintenance should include.
2 min read
Custom Software
Custom Software vs SaaS: Which Is Right for Your Business?
Evaluate fit, control, implementation speed, exit risk and total operating effort before buying or building.
2 min read
Custom Software
Essential Features of a Business Booking System
Design booking around capacity, time zones, state changes, cancellations and reliable staff operations.
2 min read